

Foundry
Fast toolkit for Ethereum development and testing
Rust toolkit (forge, cast, anvil, chisel) to build, test, fuzz and deploy Solidity contracts, with fuzz and invariant testing built in.
- Stars
- 11k
- Forks
- 2.7k
- Last commit
- today

Coverage-guided fuzzer, successor to AFL
Community-maintained successor to american fuzzy lop with faster instrumentation, custom mutators and QEMU, Frida and Unicorn modes for binaries.
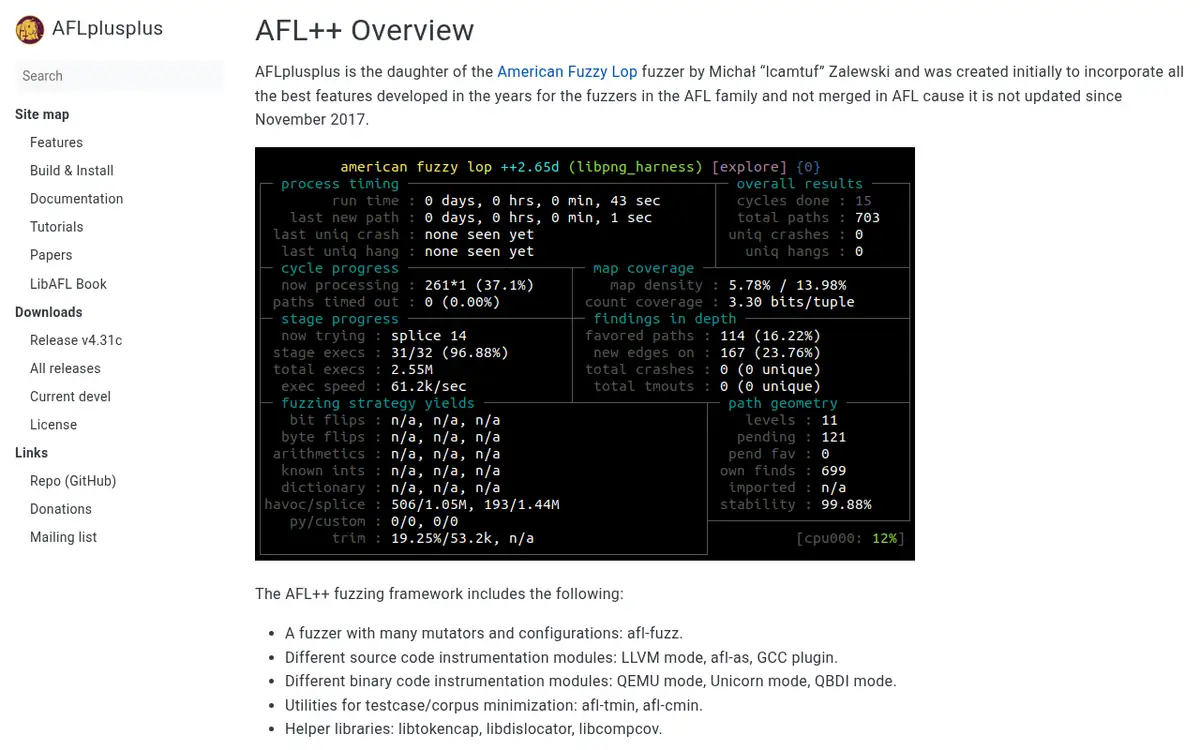
AFL++ mutates inputs and keeps those that reach new code paths, measured through compile-time instrumentation (LLVM, GCC) or binary-only modes based on QEMU, Frida and Unicorn. It adds many improvements over the original AFL, such as CmpLog, power schedules and custom mutator APIs.
It is used in research and in continuous fuzzing services such as OSS-Fuzz to find memory safety bugs and crashes.
AGPL-3.0-only · GNU AGPL v3 · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: AGPL-3.0.
No published advisory found for AFL++ in GitHub repository advisories. That does not mean the tool has no vulnerabilities.
Sources: GitHub repository advisories · checked 2026-10-20.
Fast toolkit for Ethereum development and testing
Rust toolkit (forge, cast, anvil, chisel) to build, test, fuzz and deploy Solidity contracts, with fuzz and invariant testing built in.

Property-based fuzzer for Ethereum smart contracts
Trail of Bits' fuzzer that generates transaction sequences to break user-defined invariants and assertions in Solidity contracts.