

Grype
Vulnerability scanner for images, file systems and SBOMs
Anchore's vulnerability scanner for container images, file systems and SBOMs, matching packages against a regularly updated vulnerability database.
- Stars
- 13k
- Forks
- 920
- Last commit
- today

Continuous SBOM analysis platform
OWASP platform that ingests CycloneDX SBOMs and continuously tracks component risk, vulnerabilities and licence policy across a whole portfolio.
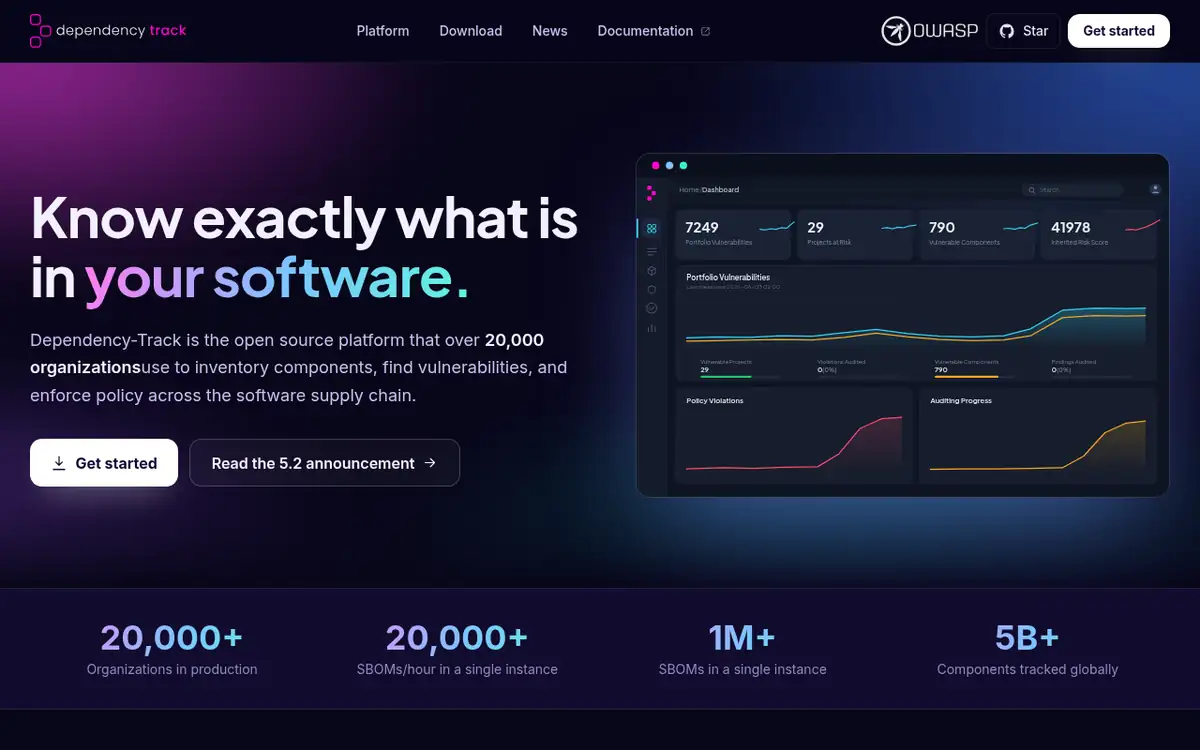
Dependency-Track stores the SBOMs of all your projects and re-evaluates them continuously as new vulnerabilities are published. It uses several intelligence sources (NVD, GitHub advisories, OSV and others) and lets teams define policies on vulnerabilities, licences and component age.
It is an OWASP flagship project and is usually fed automatically from CI with CycloneDX SBOMs through its REST API.
Apache-2.0 · Apache License 2.0 · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: Apache-2.0.
9 published advisories for Dependency-Track in GitHub repository advisories and OSV.dev. Keep the tool updated: security tools often run with broad access.
GHSA-93r8-3g93-w2gqmedium2025-11-17
Possible XML External Entity injection via validation of CycloneDX BOMs in XML format
GHSA-83g2-vgqh-mgxcCVE-2025-61776medium2025-10-07
Possible disclosure of private NuGet repository credentials to api.nuget.org
GHSA-9582-88hr-54w3CVE-2025-27137medium2025-02-24
Local file inclusion via custom notification templates
GHSA-9w3m-hm36-w32wCVE-2024-54002medium2024-12-04
Enumeration of managed users via /api/v1/user/login endpoint
GHSA-7r6q-xj4c-37g4CVE-2024-38515medium2024-06-24
Possible XML External Entity injection via upload of CycloneDX BOMs in XML format
GHSA-gh7v-4hxp-gqp4CVE-2022-39351medium2022-10-11
Logging of API keys in clear text when handling API requests using keys with insufficient permissions
GHSA-6j82-qv49-r46plow2019-12-16
Cross-Site Scripting (XSS): Persistent
GHSA-4gqv-hcmg-jw33low2019-12-16
Cross-Site Scripting (XSS): Persistent
GHSA-jp9v-w6vw-9m5vmedium2019-07-17
Cross-Site Scripting (XSS): Persistent
Sources: GitHub repository advisories, OSV.dev · checked 2026-10-20.
Vulnerability scanner for images, file systems and SBOMs
Anchore's vulnerability scanner for container images, file systems and SBOMs, matching packages against a regularly updated vulnerability database.

Dependency scanner backed by the OSV database
Google's vulnerability scanner that reads lockfiles, SBOMs and container images and checks the packages against the open OSV.dev database.

SBOM generator for images and file systems
CLI tool and Go library from Anchore that generates a software bill of materials from container images and file systems in SPDX and CycloneDX formats.

Software composition analysis for known vulnerable libraries
OWASP software composition analysis tool that identifies project dependencies and checks them for publicly disclosed vulnerabilities.

All-in-one scanner for images, code, IaC and clusters
Scanner from Aqua Security that finds vulnerabilities, misconfigurations, secrets and licences in container images, file systems, repositories and Kubernetes.

Static analysis for infrastructure as code
Policy-as-code scanner for Terraform, CloudFormation, Kubernetes, Helm, Dockerfiles and more, with graph-based checks across resources.