Skip to content
THREATWIRE

ffuf

Fast web fuzzer for content and parameter discovery

Fast web fuzzer written in Go, used to discover hidden files, directories, virtual hosts and parameters by replacing a FUZZ keyword with wordlist entries.

Open sourceMIT
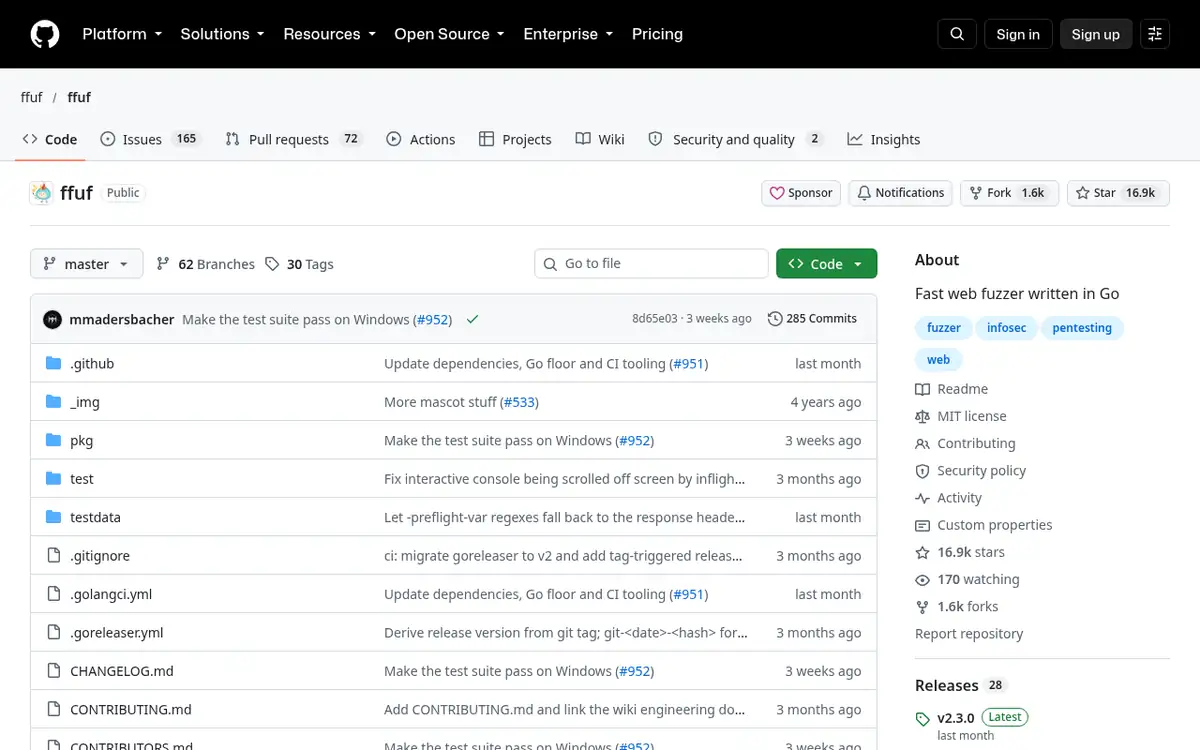
Homepage of ffuf
Official repository page, captured by ThreatWire.

What ffuf does

ffuf (Fuzz Faster U Fool) sends large numbers of HTTP requests in which a placeholder is replaced by entries from one or more wordlists. Matchers and filters on status code, size, words, lines or regular expressions separate interesting responses from noise.

It is used in web assessments and bug bounty work for content discovery, virtual host discovery and parameter fuzzing, and its JSON and CSV output makes it easy to chain with other tools.

Key features

  • Keyword-based fuzzing of URL, headers and body
  • Multiple wordlists with clusterbomb and pitchfork modes
  • Matchers and filters on status, size, words and regex
  • Recursion and auto-calibration
  • JSON, CSV, HTML and Markdown output

Licence

MIT · MIT License · Open source

Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: MIT.

Security of ffuf itself

2 published advisories for ffuf in GitHub repository advisories. Keep the tool updated: security tools often run with broad access.

  • GHSA-wc5c-g52x-g44xhigh2026-09-09

    ffuf denial of service (OOM) via an unbounded response snapshot when -od or -audit-log is enabled

  • GHSA-jcvh-xf52-2cwmCVE-2026-73232high2026-07-11

    ffuf denial of service (OOM) via HTTP response decompression bomb

Sources: GitHub repository advisories · checked 2026-10-20.

Categories and tags

Web application testingOSINT and attack surface discovery#fuzzing#content-discovery#go#cli#fuzzer#pentesting#infosec#web

Related tools

  • mitmproxy

    Interactive TLS-capable intercepting HTTP proxy

    Interactive HTTPS proxy with a terminal UI (mitmproxy), a web UI (mitmweb) and a scriptable command-line tool (mitmdump) driven by Python add-ons.

    Stars
    46k
    Forks
    4.8k
    Last commit
    today
  • sqlmap

    Automated SQL injection detection and testing

    Command-line tool that automates the detection and confirmation of SQL injection flaws in web applications, with support for many database engines.

    Stars
    39k
    Forks
    6.4k
    Last commit
    today
    GPL-2.0-or-laterOpen sourceWeb application testingDual-use
  • ZAP

    Intercepting proxy and DAST scanner for web apps

    Web application security scanner and intercepting proxy, formerly OWASP ZAP, with automated scans, a desktop UI, an API and a large add-on marketplace.

    Stars
    16k
    Forks
    2.7k
    Last commit
    4 days ago
    Apache-2.0Open sourceWeb application testing
  • Nuclei

    Template-based vulnerability scanner

    Fast vulnerability scanner driven by YAML templates, with thousands of community templates for CVEs, misconfigurations and exposures across many protocols.

    Stars
    32k
    Forks
    4k
    Last commit
    today
  • masscan

    Asynchronous TCP port scanner for large ranges

    Internet-scale port scanner that sends SYN packets asynchronously with its own TCP/IP stack, designed to scan very large address ranges quickly.

    Stars
    26k
    Forks
    3.2k
    Last commit
    14 days ago
    AGPL-3.0-onlyOpen sourceNetwork scanning and analysis
  • SpiderFoot

    OSINT automation for footprinting

    OSINT automation tool with a web UI and more than 200 modules that gather data on IPs, domains, emails, names and more from public sources.

    Stars
    24k
    Forks
    3.8k
    Last commit
    2 years ago
    Alternative toMaltego
Share on X@threatwire_https://www.threatwire.tech/tools/ffuf