

Metasploit Framework
Penetration testing framework
Rapid7's open-source framework for developing, testing and running exploit modules and auxiliary checks in authorised security assessments.
- Stars
- 39k
- Forks
- 15k
- Last commit
- today

Phishing simulation framework for awareness programmes
Open-source framework to run authorised phishing simulation campaigns, with templates, landing pages, scheduling and result tracking.
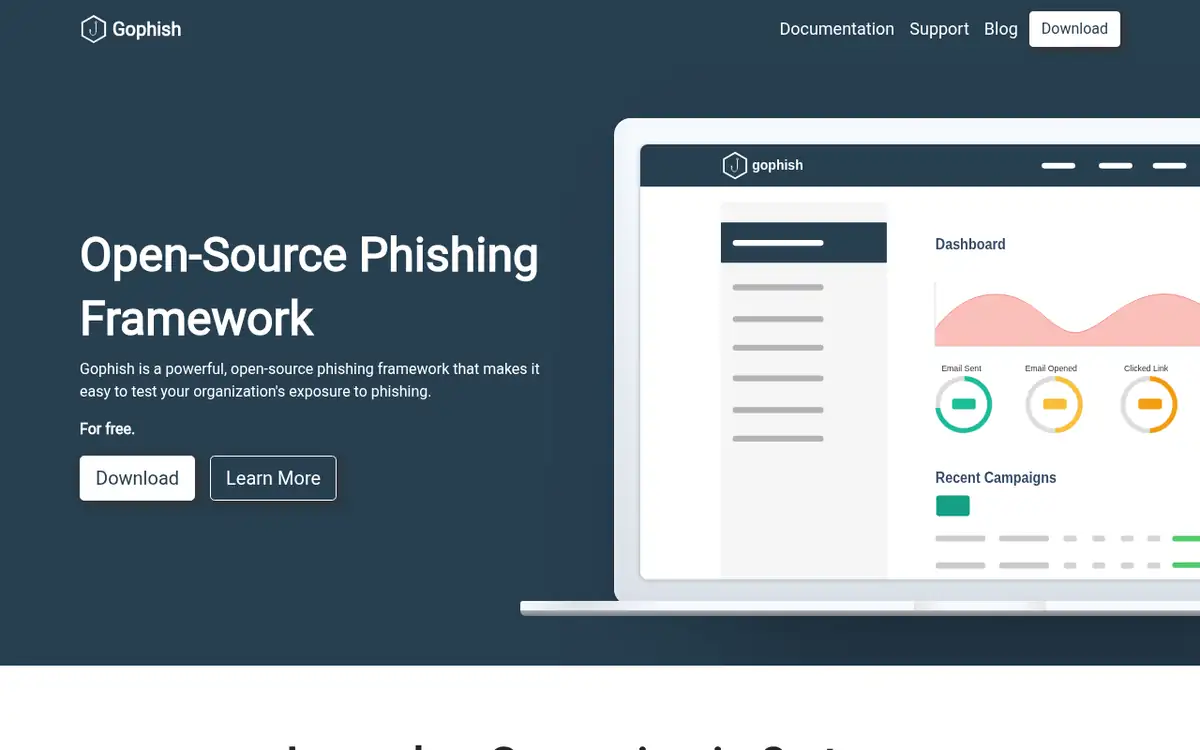
Gophish lets security teams build simulated phishing campaigns for their own organisation: email templates, landing pages, target groups and sending profiles, with a dashboard that tracks opens, clicks and reported emails.
It is used for security awareness training. It is dual-use: run campaigns only with organisational approval and in line with local law and policy.
MIT · MIT License · Open source
GitHub does not detect the licence; the LICENSE file is the MIT text for Gophish Community Edition.
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: NOASSERTION.
8 published advisories for Gophish in GitHub repository advisories and OSV.dev. Keep the tool updated: security tools often run with broad access.
GHSA-42jc-v69j-g38fCVE-2026-39904high2026-06-22
Gophish contains a denial of service vulnerability
GHSA-9f8m-9547-2gqmCVE-2025-70963moderate2026-02-06
Gophish is vulnerable to Incorrect Access Control
GHSA-rv83-h68q-c4wqCVE-2024-55196high2024-12-19
GoPhish sends cleartext passwords
GHSA-55m9-hm92-xm8jCVE-2022-45004moderate2023-03-22
Gophish vulnerable to Cross-site Scripting via crafted landing page
GHSA-8gg8-wr4j-v2wrCVE-2022-45003high2023-03-22
Gophish vulnerable to Denial of Service via crafted payload involving autofocus
GHSA-hvw3-p9px-gpc9CVE-2022-25295moderate2022-09-12
Gophish before 0.12.0 vulnerable to Open Redirect
GHSA-9c9w-9pq7-f35hCVE-2020-24710moderate2022-05-24
Gophish vulnerable to Server-Side Request Forgery
GHSA-9h9f-9q8g-6764CVE-2019-16146moderate2022-05-24
Gophish XSS Vulnerability
Sources: GitHub repository advisories, OSV.dev · checked 2026-10-20.
Penetration testing framework
Rapid7's open-source framework for developing, testing and running exploit modules and auxiliary checks in authorised security assessments.

Small detection tests mapped to MITRE ATT&CK
Red Canary's library of small, portable tests mapped to MITRE ATT&CK techniques, used to check whether detections and logging work.

Automated adversary emulation platform
Adversary emulation platform created by MITRE, now in the Apache organisation on GitHub, that runs ATT&CK-mapped operations through agents to test defences.