Skip to content
THREATWIRE

gosec

Security checker for Go source code

Inspects Go source code through its AST and SSA representation to find security problems such as injection, weak crypto and unsafe file handling.

Open sourceApache-2.0
Alternative toVeracodeCheckmarx One
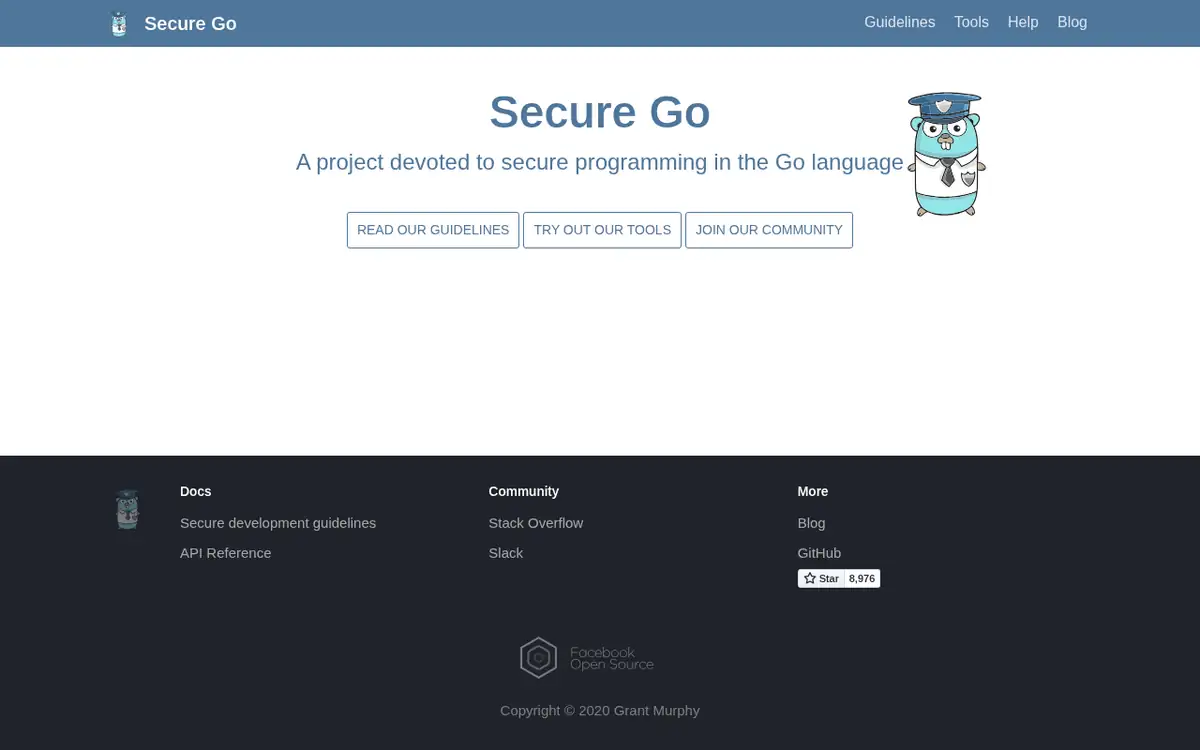
Homepage of gosec
Official website (securego.io), captured by ThreatWire.

What gosec does

gosec scans Go packages for security issues using a set of rules, each with an identifier (for example G101 for hard-coded credentials). It understands Go modules and can run on a whole project with a single command.

It is integrated into golangci-lint and available as a GitHub Action, so it often runs as part of existing Go linting.

Key features

  • Rule set covering common Go security issues
  • Go modules support
  • Annotations to suppress reviewed findings
  • Integration with golangci-lint
  • SARIF, JSON and other outputs

Licence

Apache-2.0 · Apache License 2.0 · Open source

Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: Apache-2.0.

Security of gosec itself

No published advisory found for gosec in GitHub repository advisories and OSV.dev. That does not mean the tool has no vulnerabilities.

Sources: GitHub repository advisories, OSV.dev · checked 2026-10-20.

Categories and tags

Static code analysis (SAST)#go#static-analysis#ci#linter#golang#security#security-tools#security-automation#static-code-analysis

Related tools

  • Semgrep

    Lightweight, pattern-based static analysis

    Fast static analysis engine where rules look like the code they match, supporting many languages; the open-source Community Edition runs locally and in CI.

    Stars
    17k
    Forks
    1.1k
    Last commit
    5 days ago
    LGPL-2.1-onlyOpen sourceStatic code analysis (SAST)
    Alternative toVeracodeCheckmarx One+1
  • Bandit

    Security linter for Python code

    Static analyser from the PyCQA that builds an AST of each Python file and runs plugins to flag common security issues.

    Stars
    8.3k
    Forks
    862
    Last commit
    28 days ago
    Apache-2.0Open sourceStatic code analysis (SAST)
    Alternative toVeracodeCheckmarx One
  • Slither

    Static analyser for Solidity and Vyper

    Trail of Bits' static analysis framework for Solidity and Vyper with dozens of vulnerability detectors, printers and an API for custom analyses.

    Stars
    6.4k
    Forks
    1.2k
    Last commit
    2 months ago
    AGPL-3.0-onlyOpen sourceSmart contract security
  • Aderyn

    Rust-based Solidity static analyser

    Cyfrin's static analyser for Solidity written in Rust, with detectors, Markdown audit-style reports and editor integration.

    Stars
    797
    Forks
    121
    Last commit
    5 months ago
    GPL-3.0-onlyOpen sourceSmart contract security
Share on X@threatwire_https://www.threatwire.tech/tools/gosec