Skip to content
THREATWIRE

ModSecurity

Web application firewall engine

Cross-platform WAF engine (libmodsecurity) for Apache, Nginx and IIS, typically used with the OWASP Core Rule Set. Now an OWASP project.

Open sourceApache-2.0
Alternative toCloudflare WAF
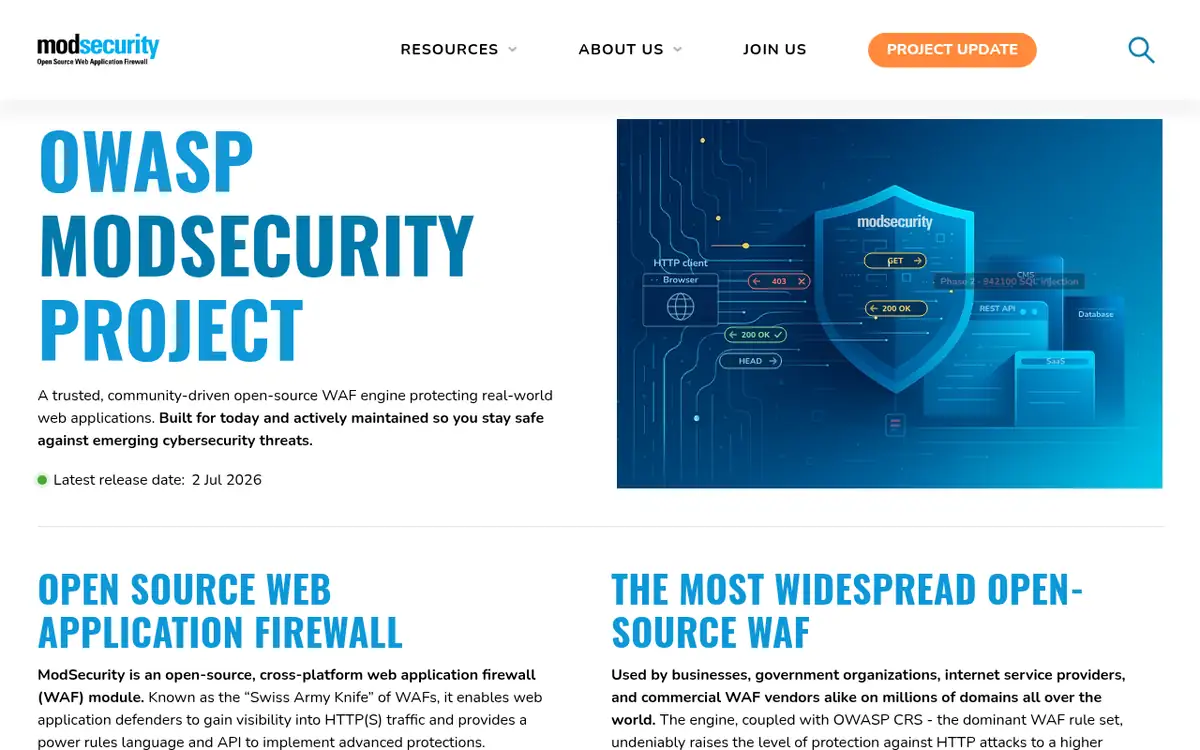
Homepage of ModSecurity
Official website (modsecurity.org), captured by ThreatWire.

What ModSecurity does

ModSecurity inspects HTTP requests and responses and applies rules written in its SecRule language. Version 3 (libmodsecurity) is a library with connectors for web servers such as Nginx and Apache. It is most often deployed with the OWASP Core Rule Set (CRS), a generic rule set against common attack classes.

In 2024 Trustwave handed the project over to OWASP, where it continues under the owasp-modsecurity organisation.

Key features

  • SecRule language and request/response inspection
  • libmodsecurity with server connectors
  • Compatible with the OWASP Core Rule Set
  • Audit logging
  • Detection-only and blocking modes

Licence

Apache-2.0 · Apache License 2.0 · Open source

Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: Apache-2.0.

Security of ModSecurity itself

17 published advisories for ModSecurity in GitHub repository advisories; the 12 most recent are listed. Keep the tool updated: security tools often run with broad access.

  • GHSA-5pww-8rfg-9crfCVE-2026-104269high2026-09-30

    RFC 2231 `filename*` Parameter Bypasses Multipart Filename Rules on RFC-Compliant Backends (Go, Python, Node, Java)

  • GHSA-4j47-8qcr-jf59medium2026-09-30

    `t:base64DecodeExt` silently discards the entire decoded value on a malformed base64 padding group, bypassing rule matching

  • GHSA-qrch-pjfr-9g47CVE-2026-104259medium2026-09-30

    removeComments Transformation Fails to Strip Adjacent Comments, Enabling WAF Rule Bypass

  • GHSA-5m93-4h75-3p2wCVE-2026-103932medium2026-09-30

    PCRE2 `@rxGlobal` match-limit errors are converted to no-match

  • GHSA-jx3r-phvx-2jmjCVE-2026-73857high2026-09-30

    ModSecurity v3 XML Request Body Processor Uninitialized Pointer Dereference Vulnerability

  • GHSA-vmg8-j66p-vgvwCVE-2026-73856high2026-09-30

    Response Body Inspection Bypass

  • GHSA-2vqc-36qp-ccmwCVE-2026-61813low2026-09-30

    Incorrect libcurl TLS hostname verification setting in HttpsClient::download

  • GHSA-cxqf-vgrr-xxrvCVE-2026-61812medium2026-09-30

    HTML decoder missing entities, leading to evasion

  • GHSA-qjgm-7gp4-f8qqCVE-2026-52761medium2026-06-29

    Transformation utf8toUnicode produces wrong output on i386 architecture

  • GHSA-rcw9-2f5r-7p88CVE-2026-52747high2026-06-29

    Multipart form-data parser silently strips embedded line breaks from form-field values, enabling request-body inspection bypass

  • GHSA-vwr3-7x7g-7p9wCVE-2026-42268high2026-04-28

    Unsigned integer underflow in @verifySSN / @verifyCPF / @verifySVNR operators

  • GHSA-qrjc-3jpc-3h2gCVE-2026-30923high2026-04-28

    libModSecurity3: Segfault on query strings with a single character when using `t:hexDecode`

Sources: GitHub repository advisories · checked 2026-10-20.

Categories and tags

WAF and edge protection#waf#owasp-crs#nginx#apache#modsecurity#apache2

Related tools

  • CrowdSec

    Collaborative behaviour-based IPS

    Security engine that parses logs to detect aggressive behaviour, blocks it with remediation components and shares signals in a community blocklist.

    Stars
    15k
    Forks
    745
    Last commit
    today
    Alternative toCloudflare WAF
  • BunkerWeb

    Nginx-based web application firewall

    WAF and hardened reverse proxy based on Nginx, with ModSecurity and the OWASP CRS, bot protection and a web UI, for Docker, Kubernetes or Linux.

    Stars
    11k
    Forks
    655
    Last commit
    5 days ago
    AGPL-3.0-onlyOpen sourceWAF and edge protection
    Alternative toCloudflare WAF
  • Coraza

    ModSecurity-compatible WAF library in Go

    OWASP WAF library written in Go, compatible with ModSecurity SecLang rules and the OWASP Core Rule Set, embeddable in Go apps and proxies.

    Stars
    3.9k
    Forks
    370
    Last commit
    today
    Apache-2.0Open sourceWAF and edge protection
    Alternative toCloudflare WAF
Share on X@threatwire_https://www.threatwire.tech/tools/modsecurity