

Foundry
Fast toolkit for Ethereum development and testing
Rust toolkit (forge, cast, anvil, chisel) to build, test, fuzz and deploy Solidity contracts, with fuzz and invariant testing built in.
- Stars
- 11k
- Forks
- 2.7k
- Last commit
- today

Symbolic execution analyser for EVM bytecode
Security analysis tool from Consensys Diligence that uses symbolic execution and SMT solving to find vulnerabilities in EVM bytecode.
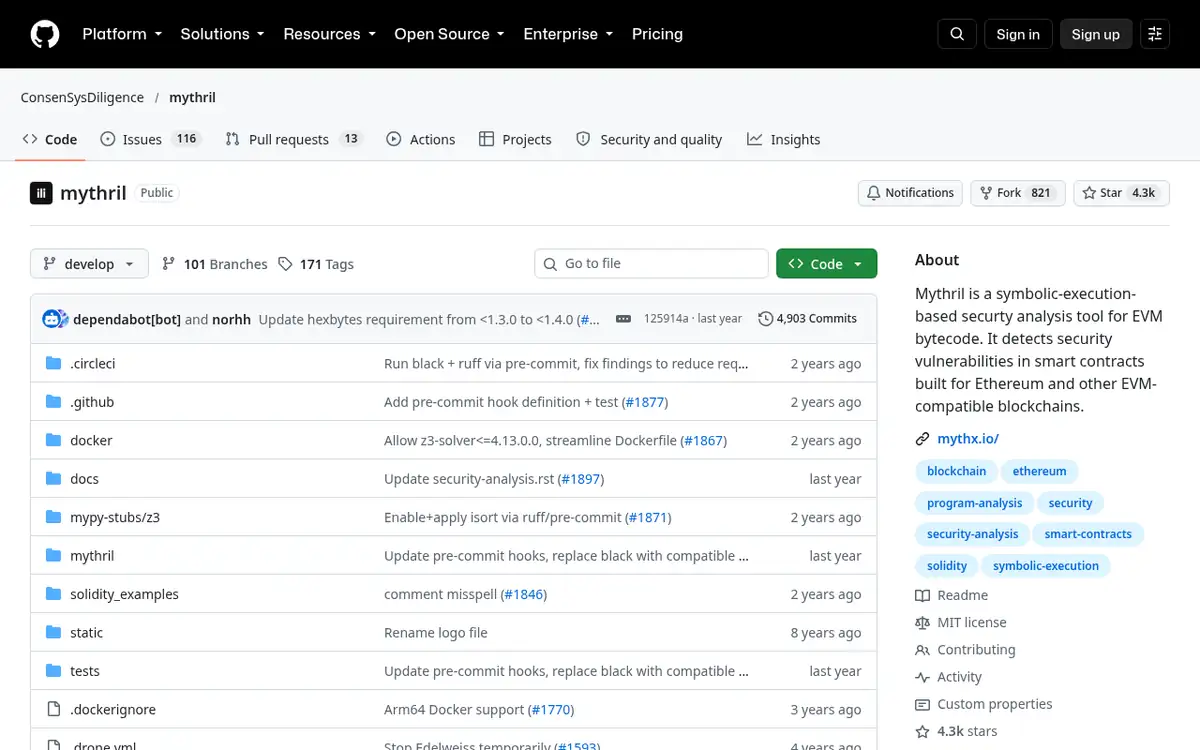
Mythril explores the possible execution paths of EVM bytecode with symbolic execution and an SMT solver to detect issues such as integer overflows, unprotected self-destruct, reentrancy patterns and unchecked calls. It can analyse Solidity source, compiled bytecode or contracts deployed on-chain.
Analysis depth is configurable through transaction count and timeouts, trading speed for coverage.
MIT · MIT License · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: MIT.
No published advisory found for Mythril in GitHub repository advisories and OSV.dev. That does not mean the tool has no vulnerabilities.
Sources: GitHub repository advisories, OSV.dev · checked 2026-10-20.
Fast toolkit for Ethereum development and testing
Rust toolkit (forge, cast, anvil, chisel) to build, test, fuzz and deploy Solidity contracts, with fuzz and invariant testing built in.

Static analyser for Solidity and Vyper
Trail of Bits' static analysis framework for Solidity and Vyper with dozens of vulnerability detectors, printers and an API for custom analyses.

Property-based fuzzer for Ethereum smart contracts
Trail of Bits' fuzzer that generates transaction sequences to break user-defined invariants and assertions in Solidity contracts.

Symbolic testing for EVM smart contracts
a16z's symbolic testing tool that runs Foundry-style tests with symbolic inputs to prove properties or find counterexamples.

Rust-based Solidity static analyser
Cyfrin's static analyser for Solidity written in Rust, with detectors, Markdown audit-style reports and editor integration.