

Nuclei
Template-based vulnerability scanner
Fast vulnerability scanner driven by YAML templates, with thousands of community templates for CVEs, misconfigurations and exposures across many protocols.
- Stars
- 32k
- Forks
- 4k
- Last commit
- today
Web server scanner for dangerous files and misconfigurations
Long-running open-source web server scanner that checks for dangerous files, outdated server software and common misconfigurations.
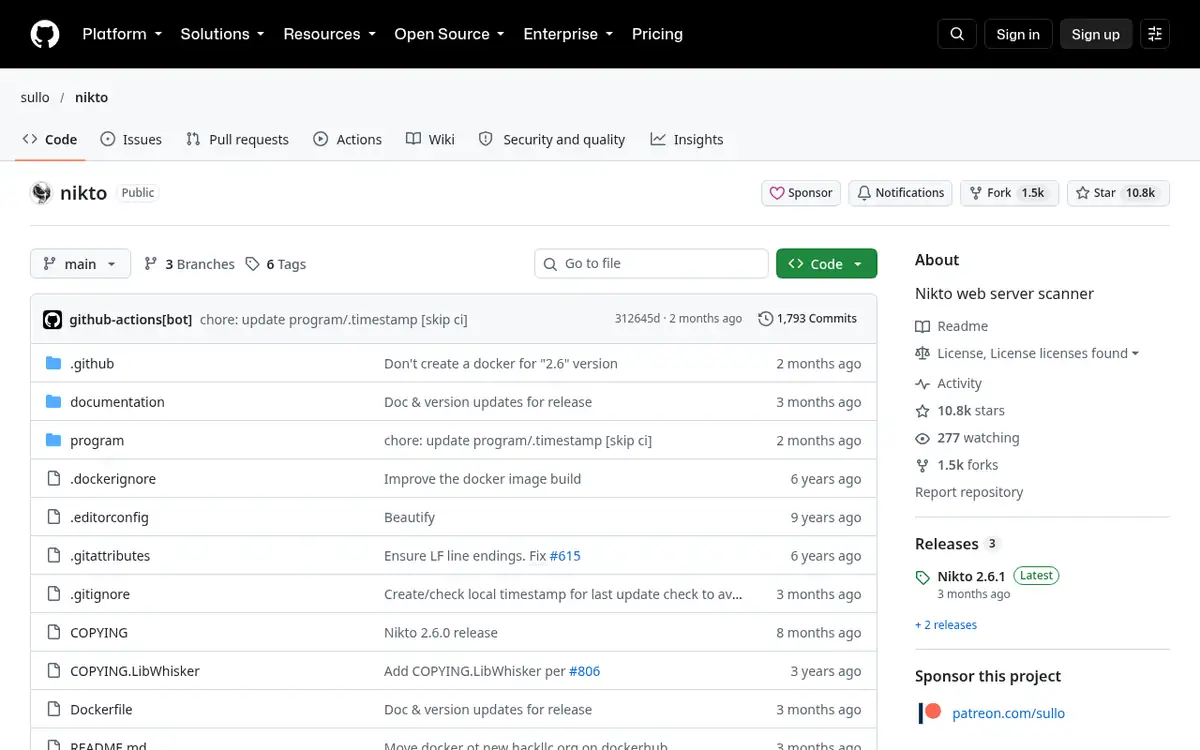
Nikto performs a broad set of checks against a web server: default and dangerous files, outdated versions of server software, version-specific problems and server configuration items such as risky HTTP options. It is noisy by design and is meant for quick baseline checks rather than stealth.
Written in Perl, it has been maintained by Chris Sullo for more than two decades and remains a common first pass in web infrastructure assessments.
GPL-3.0-only · GNU GPL v3 (code); database files under separate terms · Open source
The COPYING file licenses Nikto's code under GPL v3; its check database files are not GPL and may only be distributed with the official Nikto package.
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: NOASSERTION.
No published advisory found for Nikto in GitHub repository advisories. That does not mean the tool has no vulnerabilities.
Sources: GitHub repository advisories · checked 2026-10-20.
Template-based vulnerability scanner
Fast vulnerability scanner driven by YAML templates, with thousands of community templates for CVEs, misconfigurations and exposures across many protocols.

Vulnerability management and DevSecOps findings platform
Web platform that imports findings from many security scanners, deduplicates them and tracks remediation across products and engagements.

Network vulnerability scanner (Greenbone Community Edition)
Scanner engine of the Greenbone Community Edition, running network vulnerability tests from the Greenbone community feed against hosts and services.

Intercepting proxy and DAST scanner for web apps
Web application security scanner and intercepting proxy, formerly OWASP ZAP, with automated scans, a desktop UI, an API and a large add-on marketplace.

Interactive TLS-capable intercepting HTTP proxy
Interactive HTTPS proxy with a terminal UI (mitmproxy), a web UI (mitmweb) and a scriptable command-line tool (mitmdump) driven by Python add-ons.

Penetration testing framework
Rapid7's open-source framework for developing, testing and running exploit modules and auxiliary checks in authorised security assessments.