Skip to content
THREATWIRE

Zeek

Network security monitoring and traffic analysis framework

Network analysis framework, formerly Bro, that turns traffic into rich, structured logs of connections and protocols, with its own scripting language.

Open sourceBSD-3-Clause
Alternative toDarktrace
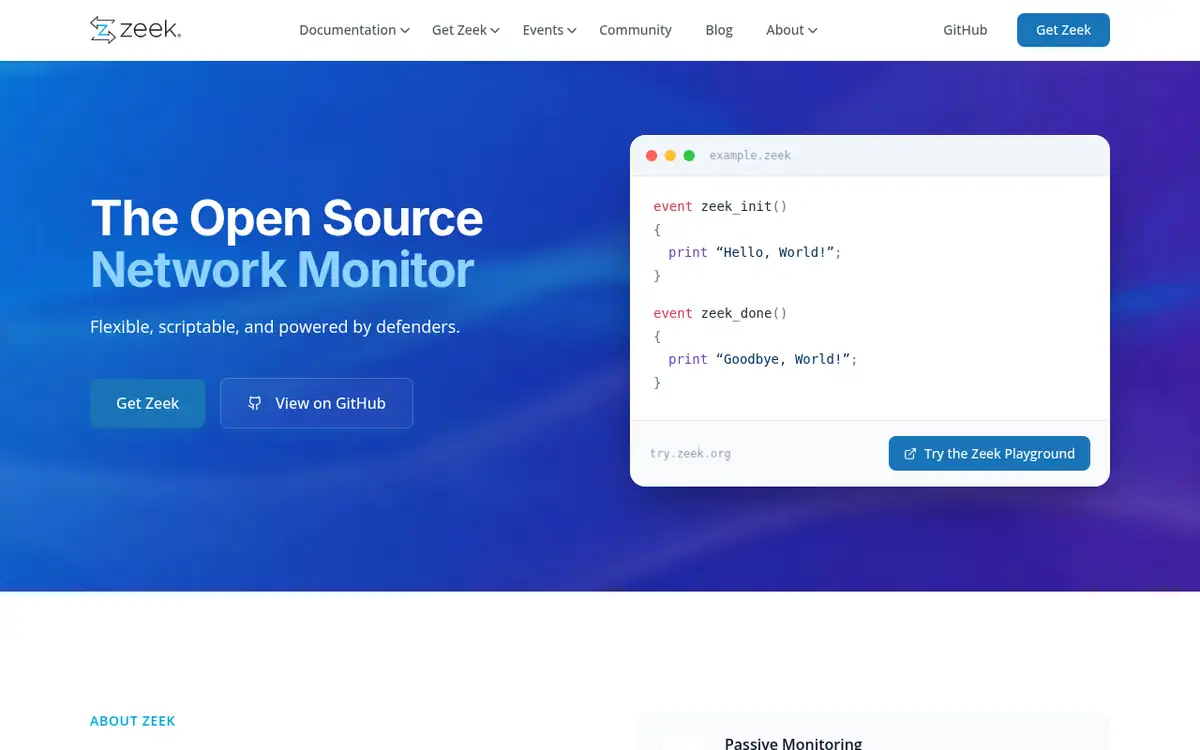
Homepage of Zeek
Official website (zeek.org), captured by ThreatWire.

What Zeek does

Zeek observes network traffic passively and writes structured logs that describe what happened: connections, DNS queries, HTTP requests, TLS certificates, files and much more. Instead of only signature alerts, it gives analysts a detailed record of network activity for detection, hunting and forensics.

Its event-driven scripting language lets teams write custom detections and protocol analysis, and a package manager distributes community extensions. Zeek is often deployed next to a signature IDS such as Suricata.

Key features

  • Detailed logs for many network protocols
  • Event-driven scripting language
  • Package manager for community extensions
  • Cluster deployment for high-volume links
  • File analysis and intelligence framework

Licence

BSD-3-Clause · BSD 3-Clause License · Open source

GitHub does not detect the licence; the COPYING file is the BSD 3-clause text.

Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: NOASSERTION.

Security of Zeek itself

25 published advisories for Zeek in GitHub repository advisories; the 12 most recent are listed. Keep the tool updated: security tools often run with broad access.

Sources: GitHub repository advisories · checked 2026-10-20.

Categories and tags

Related tools

  • Suricata

    Network IDS, IPS and security monitoring engine

    High-performance network threat detection engine from the OISF: signature-based IDS/IPS, protocol logging and file extraction in one multi-threaded engine.

    Stars
    6.8k
    Forks
    1.8k
    Last commit
    today
    GPL-2.0-onlyOpen sourceIDS, IPS and network monitoring
    Alternative toDarktrace
  • Snort 3

    Rule-based network intrusion prevention system

    The next generation of the Snort IPS, maintained by Cisco Talos: multi-threaded, with a new rule parser and Lua-based configuration.

    Stars
    3.4k
    Forks
    691
    Last commit
    5 months ago
    GPL-2.0-onlyOpen sourceIDS, IPS and network monitoring
    Alternative toDarktrace
  • Wireshark

    Network protocol analyser

    The widely used network protocol analyser: capture live traffic or open capture files and inspect thousands of protocols with display filters.

    Stars
    10k
    Forks
    2.2k
    Last commit
    today
    GPL-2.0-onlyOpen sourceNetwork scanning and analysis
  • mitmproxy

    Interactive TLS-capable intercepting HTTP proxy

    Interactive HTTPS proxy with a terminal UI (mitmproxy), a web UI (mitmweb) and a scriptable command-line tool (mitmdump) driven by Python add-ons.

    Stars
    46k
    Forks
    4.8k
    Last commit
    today
  • masscan

    Asynchronous TCP port scanner for large ranges

    Internet-scale port scanner that sends SYN packets asynchronously with its own TCP/IP stack, designed to scan very large address ranges quickly.

    Stars
    26k
    Forks
    3.2k
    Last commit
    14 days ago
    AGPL-3.0-onlyOpen sourceNetwork scanning and analysis
Share on X@threatwire_https://www.threatwire.tech/tools/zeek