Skip to content
THREATWIRE

Falco

Runtime threat detection for containers and hosts

CNCF graduated project that watches Linux system calls (via eBPF or a kernel module) and raises alerts when rules detect suspicious behaviour.

Open sourceApache-2.0
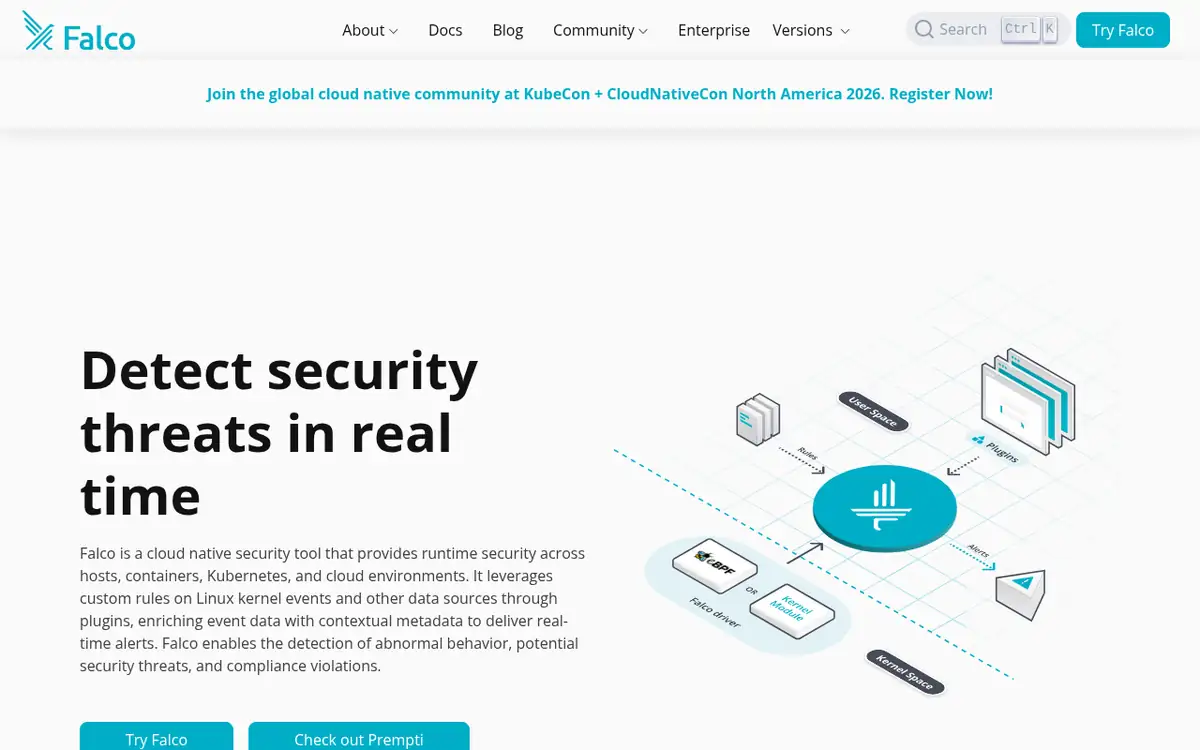
Homepage of Falco
Official website (falco.org), captured by ThreatWire.

What Falco does

Falco collects kernel events such as system calls and enriches them with container and Kubernetes metadata. Rules written in YAML describe suspicious behaviour, for example a shell spawned inside a container or an unexpected write to a sensitive directory, and Falco emits an alert when they match.

It also ingests other event sources through plugins, such as Kubernetes audit logs and cloud audit trails. Falco is a graduated project of the Cloud Native Computing Foundation.

Key features

  • Kernel event collection with modern eBPF probe
  • YAML rules with a default rule set
  • Container and Kubernetes metadata enrichment
  • Plugins for audit logs and other sources
  • Falcosidekick to forward alerts

Licence

Apache-2.0 · Apache License 2.0 · Open source

Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: Apache-2.0.

Security of Falco itself

8 published advisories for Falco in GitHub repository advisories and OSV.dev. Keep the tool updated: security tools often run with broad access.

Sources: GitHub repository advisories, OSV.dev · checked 2026-10-20.

Categories and tags

Container and Kubernetes securityEndpoint visibility and response#runtime-security#ebpf#kubernetes#cncf#containers#security#falco

Related tools

  • Trivy

    All-in-one scanner for images, code, IaC and clusters

    Scanner from Aqua Security that finds vulnerabilities, misconfigurations, secrets and licences in container images, file systems, repositories and Kubernetes.

    Stars
    39k
    Forks
    776
    Last commit
    today
    Alternative toSnykPrisma Cloud+1
  • Kubescape

    Kubernetes security posture and compliance scanner

    CNCF project that scans clusters, manifests and Helm charts against frameworks such as the NSA-CISA guidance and CIS Benchmarks, and scans images.

    Stars
    12k
    Forks
    1.1k
    Last commit
    today
    Alternative toWizPrisma Cloud
  • kube-bench

    CIS Kubernetes Benchmark checks

    Aqua Security tool that checks whether Kubernetes nodes and control-plane components are configured according to the CIS Kubernetes Benchmark.

    Stars
    8.2k
    Forks
    1.3k
    Last commit
    14 days ago
  • osquery

    Query your endpoints with SQL

    Exposes the operating system as a relational database so processes, users, packages and configuration can be queried with SQL on Linux, macOS and Windows.

    Stars
    24k
    Forks
    2.6k
    Last commit
    4 days ago
    Apache-2.0 OR GPL-2.0-onlyOpen sourceEndpoint visibility and response
    Alternative toCrowdStrike Falcon
Share on X@threatwire_https://www.threatwire.tech/tools/falco