Skip to content
THREATWIRE

Wazuh

Open-source XDR and SIEM platform

Security platform combining an endpoint agent, a manager and an indexer for log analysis, intrusion detection, file integrity monitoring and compliance.

Open sourceGPL-2.0-only AND AGPL-3.0-or-later
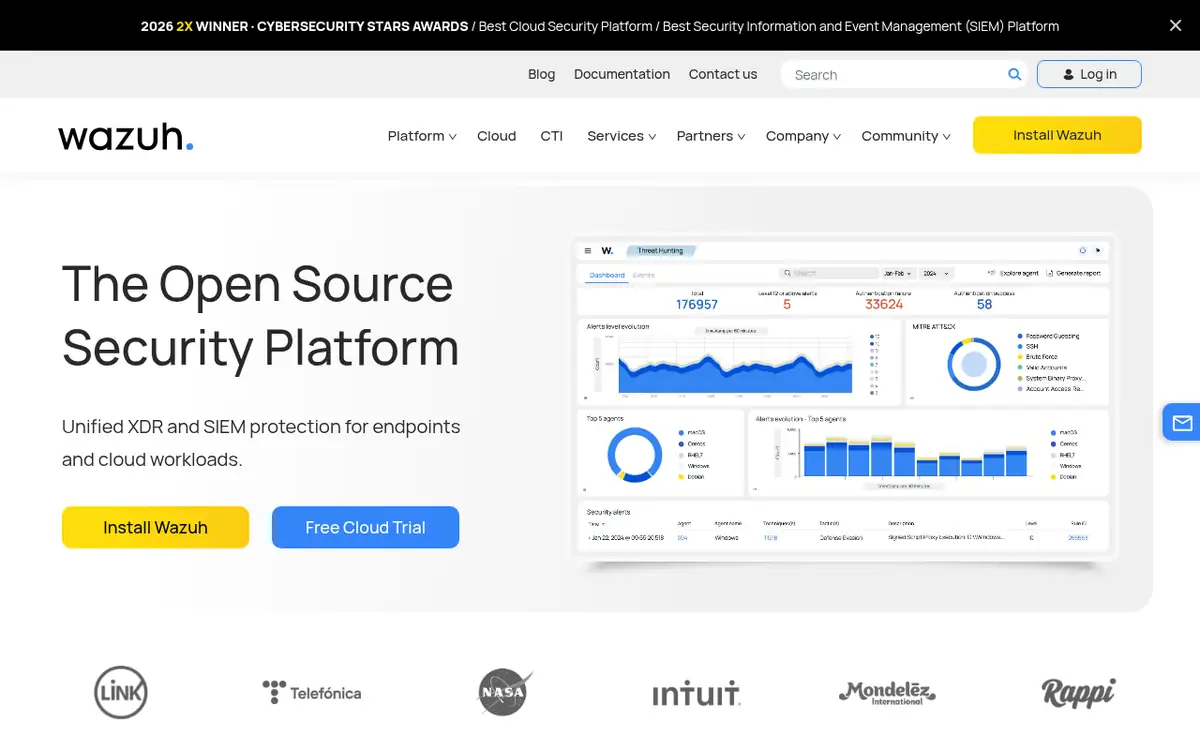
Homepage of Wazuh
Official website (wazuh.com), captured by ThreatWire.

What Wazuh does

Wazuh agents run on Linux, Windows and macOS endpoints and send events to a central manager, which applies decoders and rules to raise alerts. The platform covers log analysis, file integrity monitoring, vulnerability detection, configuration assessment and active response, with dashboards built on the Wazuh indexer.

It grew out of a fork of OSSEC and is now one of the most widely deployed open-source SIEM/XDR stacks. Wazuh Inc. offers a hosted cloud version and support.

Key features

  • Endpoint agents for Linux, Windows and macOS
  • Rule-based log analysis and alerting
  • File integrity monitoring and vulnerability detection
  • Security configuration assessment and compliance mapping
  • Indexer and dashboards for search and visualisation

Licence

GPL-2.0-only AND AGPL-3.0-or-later · GNU GPL v2 (with OpenSSL exception) and GNU AGPL v3 for the engine · Open source

GitHub does not detect the licence. Per the LICENSE file, the engine under src/engine is AGPL-3.0-or-later, some shared libraries are GPL-2.0-only OR AGPL-3.0-or-later, and the rest is GPL v2.

Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: NOASSERTION.

Security of Wazuh itself

88 published advisories for Wazuh in GitHub repository advisories; the 12 most recent are listed. Keep the tool updated: security tools often run with broad access.

  • GHSA-cjf8-wjx6-hjw6CVE-2026-74041critical2026-10-13

    Case-sensitivity mismatch bypasses remote-command validation, allowing command execution as root

  • GHSA-vc33-wcqf-cwgvCVE-2026-74033medium2026-10-13

    Missing destination-path validation in CDB list cluster-callable handlers allows arbitrary file read/delete on the manager

  • GHSA-3xm6-wp5v-2fm9CVE-2026-74037high2026-10-13

    Improper session invalidation in check_token: revoking a run_as user's administrator grant does not invalidate their token, enabling permanent self-re-grant of administrator

  • GHSA-27gv-q7q6-f5qhCVE-2026-74035high2026-10-13

    An empty password bypasses both the password policy and the reserved user guard in `security.update_user`, allowing a delegated user administrator to take over the `wazuh` superuser account

  • GHSA-gc4j-j9fg-4cfrCVE-2026-74045high2026-10-13CVE-2026-74045 in the tracker on ThreatWire

    Heap buffer overflow in wazuh-analysisd fim_generate_alert() lets an enrolled agent corrupt manager heap memory and terminate the analysis engine

  • GHSA-crrg-5qvw-8wjxCVE-2026-93346medium2026-10-13

    API brute-force protection is still bypassable by concurrent login requests, the `asyncio.Lock` fix for GHSA-m2mr-xhhv-jx58 serializes the counter but does not close the check-then-count race

  • GHSA-qmhg-366r-jjfpCVE-2026-74036high2026-10-13CVE-2026-74036 in the tracker on ThreatWire

    Remote code execution as root on Wazuh agents via SCA command policies

  • GHSA-xrjw-cqrv-j92gCVE-2026-93347medium2026-10-13

    Path traversal in cluster-callable get_list_file allows arbitrary file read as the wazuh user

  • GHSA-w4qc-m4j4-6m9cCVE-2026-74031medium2026-10-13

    Path traversal in cluster-callable rule/decoder delete helpers allows arbitrary file deletion as the wazuh user

  • GHSA-r7hm-43xr-477jCVE-2026-74034high2026-10-13

    Arbitrary file read as root via agent-injected upgrade_custom command

  • GHSA-qj8j-r988-54rxCVE-2026-74047medium2026-10-13

    authd.pass disclosed to low-privileged users through the per-agent active configuration endpoint

  • GHSA-vh8p-3xvw-w536CVE-2026-74032medium2026-10-13

    RBAC Authorization Bypass in Wazuh API

Sources: GitHub repository advisories · checked 2026-10-20.

Categories and tags

SIEM, XDR and log managementEndpoint visibility and response#siem#xdr#hids#agent#compliance#security#log-analysis#vulnerability-detection#cybersecurity#file-integrity-monitoring

Related tools

Share on X@threatwire_https://www.threatwire.tech/tools/wazuh