

OpenCTI
Cyber threat intelligence knowledge platform
Platform by Filigran to structure, store and visualise threat intelligence as a STIX 2.1 knowledge graph, with many connectors.
- Stars
- 10k
- Forks
- 1.5k
- Last commit
- today
Alternative toRecorded Future

Threat intelligence sharing platform
Open-source platform to store, correlate and share indicators and threat information within and between organisations and communities.
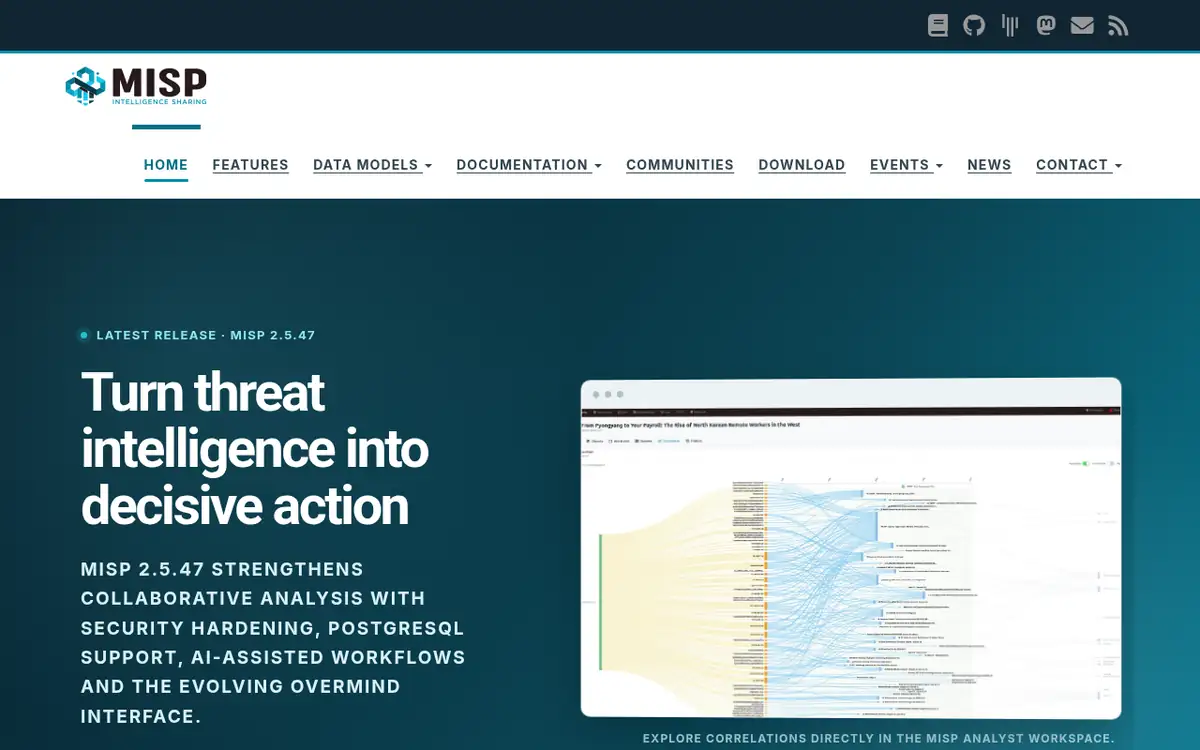
MISP stores events made of attributes (indicators such as hashes, IPs and domains) and objects, correlates them automatically and shares them with connected instances according to distribution rules. Taxonomies and galaxies (threat actors, malware, ATT&CK techniques) give context.
It is used by CERTs, ISACs and security teams worldwide; development is led by CIRCL, the Computer Incident Response Center Luxembourg.
AGPL-3.0-only · GNU AGPL v3 · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: AGPL-3.0.
4 published advisories for MISP in GitHub repository advisories. Keep the tool updated: security tools often run with broad access.
GHSA-4cxp-22wm-j6jrCVE-2026-44381critical2026-04-29
MISP - SQL injection via unvalidated ordering parameters in event and shadow attribute listings
GHSA-3939-4g6m-m3hcCVE-2026-44380high2026-04-29
MISP - Improper access control in auth key reset allows privilege escalation to site administrator
GHSA-jrvj-84mg-8f29CVE-2026-44379medium2026-04-29
Improper UUID validation in MISP Collections
GHSA-mc53-48w8-9g63CVE-2026-39962high2026-04-08
LDAP injection in MISP ApacheAuthenticate when using a user-controlled Apache environment variable
Sources: GitHub repository advisories · checked 2026-10-20.
Cyber threat intelligence knowledge platform
Platform by Filigran to structure, store and visualise threat intelligence as a STIX 2.1 knowledge graph, with many connectors.
OSINT automation for footprinting
OSINT automation tool with a web UI and more than 200 modules that gather data on IPs, domains, emails, names and more from public sources.

Pattern matching for malware research
Tool and rule language from VirusTotal to identify and classify malware samples using textual and binary patterns plus conditions.