

radare2
UNIX-like reverse engineering framework
Command-line reverse engineering framework with a disassembler, debugger, hex editor and scripting for many architectures and file formats.
- Stars
- 25k
- Forks
- 3.4k
- Last commit
- today
Alternative toIDA Pro

Pattern matching for malware research
Tool and rule language from VirusTotal to identify and classify malware samples using textual and binary patterns plus conditions.
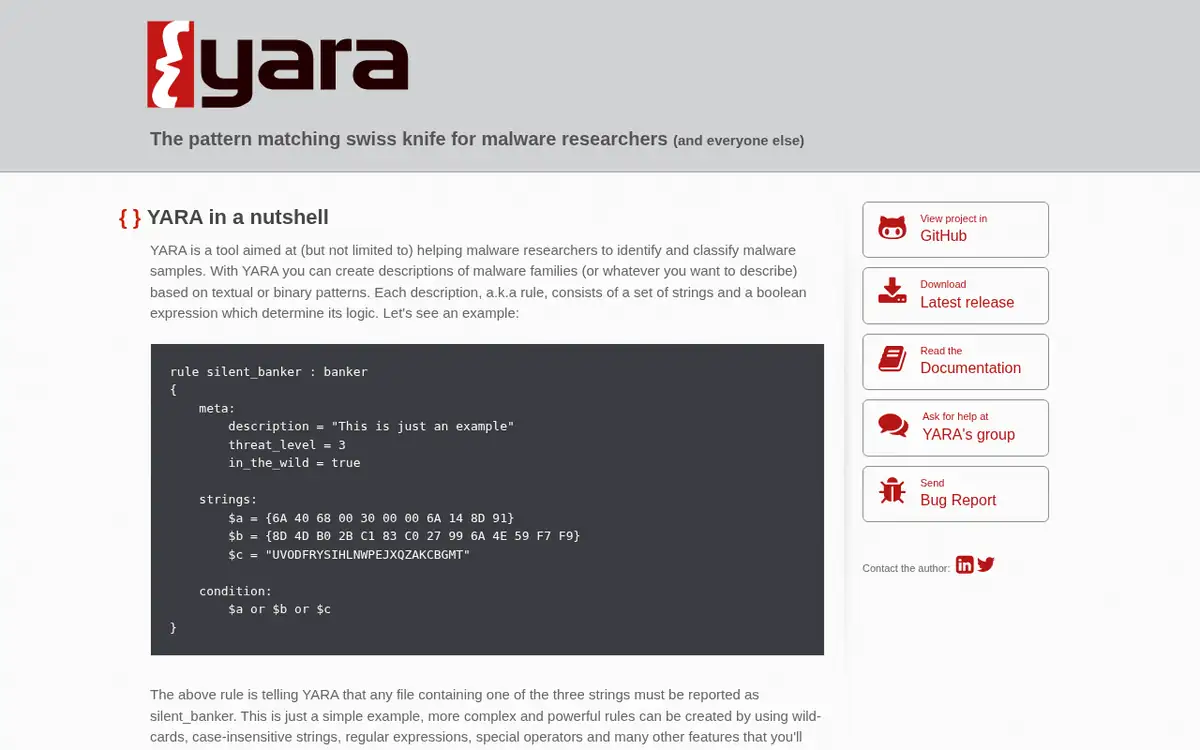
YARA rules describe families of malware or other files with strings, hex patterns and boolean conditions, and modules expose file metadata (PE, ELF, hashes, math). The engine scans files or process memory and reports which rules match.
YARA rules are a common way to share detection logic in threat intelligence. VirusTotal also develops YARA-X, a Rust rewrite, in a separate repository.
BSD-3-Clause · BSD 3-Clause License · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: BSD-3-Clause.
No published advisory found for YARA in GitHub repository advisories. That does not mean the tool has no vulnerabilities.
Sources: GitHub repository advisories · checked 2026-10-20.
UNIX-like reverse engineering framework
Command-line reverse engineering framework with a disassembler, debugger, hex editor and scripting for many architectures and file formats.
Software reverse engineering framework from the NSA
Reverse engineering suite released by the NSA with disassembly, decompilation, graphing and scripting for many processor architectures.

Memory forensics framework
Framework for extracting digital artefacts from memory images (RAM dumps) of Windows, Linux and macOS systems, rewritten in Python 3.
Reverse engineering tool for Android APK files
Decodes Android APK resources and code to a near-original form (smali) and rebuilds them after modification, for analysis and testing.

Query your endpoints with SQL
Exposes the operating system as a relational database so processes, users, packages and configuration can be queried with SQL on Linux, macOS and Windows.
OSINT automation for footprinting
OSINT automation tool with a web UI and more than 200 modules that gather data on IPs, domains, emails, names and more from public sources.