

Frida
Dynamic instrumentation toolkit
Injects a JavaScript engine into running processes on Windows, macOS, Linux, iOS and Android to trace, hook and modify functions at runtime.
- Stars
- 22k
- Forks
- 2.3k
- Last commit
- today
Alternative toNowSecure
Reverse engineering tool for Android APK files
Decodes Android APK resources and code to a near-original form (smali) and rebuilds them after modification, for analysis and testing.
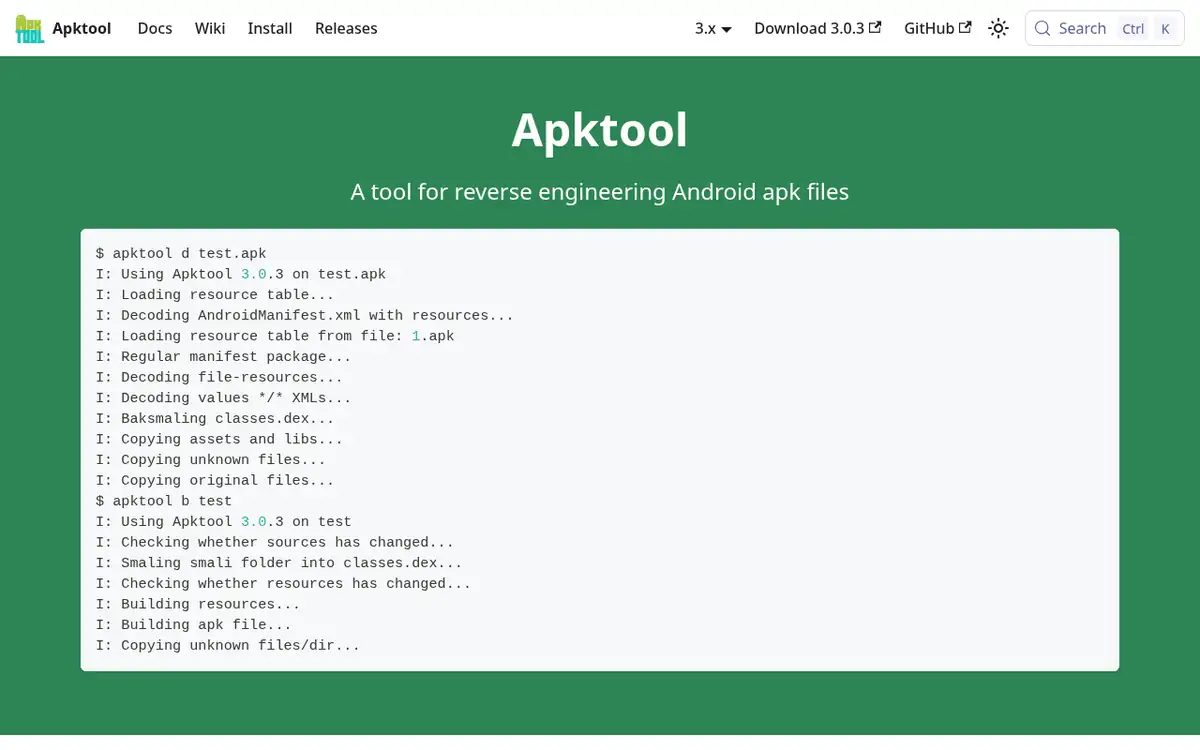
Apktool decodes the resources of an APK (manifest, layouts, strings) into readable files and disassembles the Dalvik bytecode into smali. After changes, it can rebuild the APK, which is useful for security testing, localisation and debugging.
It is a building block of many Android analysis workflows and tools.
Apache-2.0 · Apache License 2.0 · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: Apache-2.0.
3 published advisories for Apktool in GitHub repository advisories. Keep the tool updated: security tools often run with broad access.
GHSA-m8mh-x359-vm8mCVE-2026-39973high2026-04-19
Path Traversal to Arbitrary File Write in Apktool 3.0.1 (Regression in commit e10a045)
GHSA-vgwr-4w3p-xmjvhigh2024-01-20
Write to arbitrary files while decoding on Windows
GHSA-2hqv-2xv4-5h5wCVE-2024-21633high2024-01-03
Arbitrary file write on Decoding
Sources: GitHub repository advisories · checked 2026-10-20.
Dynamic instrumentation toolkit
Injects a JavaScript engine into running processes on Windows, macOS, Linux, iOS and Android to trace, hook and modify functions at runtime.

Automated mobile app security testing
Mobile Security Framework: automated static and dynamic analysis of Android and iOS apps, with malware analysis and a REST API for CI.
Software reverse engineering framework from the NSA
Reverse engineering suite released by the NSA with disassembly, decompilation, graphing and scripting for many processor architectures.

UNIX-like reverse engineering framework
Command-line reverse engineering framework with a disassembler, debugger, hex editor and scripting for many architectures and file formats.

Pattern matching for malware research
Tool and rule language from VirusTotal to identify and classify malware samples using textual and binary patterns plus conditions.

Memory forensics framework
Framework for extracting digital artefacts from memory images (RAM dumps) of Windows, Linux and macOS systems, rewritten in Python 3.