

radare2
UNIX-like reverse engineering framework
Command-line reverse engineering framework with a disassembler, debugger, hex editor and scripting for many architectures and file formats.
- Stars
- 25k
- Forks
- 3.4k
- Last commit
- today
Alternative toIDA Pro
Software reverse engineering framework from the NSA
Reverse engineering suite released by the NSA with disassembly, decompilation, graphing and scripting for many processor architectures.
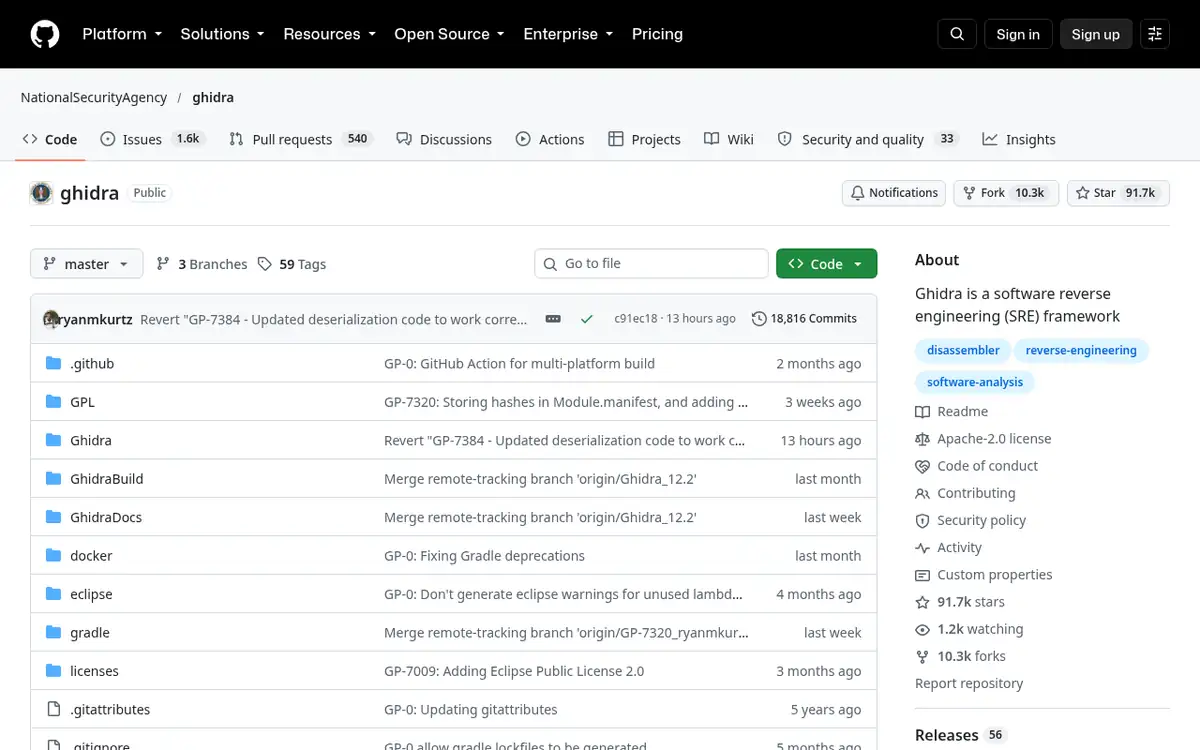
Ghidra analyses compiled code for a wide range of processor families and executable formats. Its decompiler produces C-like pseudo-code, and the suite includes graphing, patching, version tracking between binaries and collaborative analysis through a shared server.
It is extensible with Java and Python scripts and plugins. The US National Security Agency released it as open source in 2019 and continues to develop it in public.
Apache-2.0 · Apache License 2.0 · Open source
Checked by ThreatWire against the repository's licence file on 2026-10-20. GitHub detects: Apache-2.0.
33 published advisories for Ghidra in GitHub repository advisories; the 12 most recent are listed. Keep the tool updated: security tools often run with broad access.
GHSA-c3pf-92jf-vq96medium2026-09-22
Arbitrary Code Execution via uncontrolled search path in the Swift Demangler analyzer (Windows)
GHSA-vxmq-6v38-hgf6medium2026-09-22
Denial of Service, Cyclic x64 chained unwind metadata causes StackOverflowError during PE import
GHSA-4w7g-wmg8-fgv5CVE-2026-96273medium2026-09-22
Improper Array Index Validation in DB Unregistered Options parsing Leads to unreleased lock and Denial of Service
GHSA-2697-fm9m-mqvwmedium2026-08-19
Infinite loop (uncontrolled resource consumption) in PEF loader — crafted PEF hangs Ghidra on import
GHSA-3f3p-5h4j-gq2rmedium2026-08-19
Path Traversal in XmlLoader Allows Arbitrary Local File Read During XML Import
GHSA-pcfh-853f-q3ghCVE-2026-18718high2026-08-19
Conditional Arbitrary Code Execution via Swift Demangler Analyzer (ACE)
GHSA-f5gv-pxqw-x95wmedium2026-08-19
Dyld cache mappingCount causes unbounded heap allocation during import load-spec discovery
GHSA-f75p-8cqj-9v3gCVE-2026-54389medium2026-08-19
PDB Parser Resource Consumption
GHSA-42gp-j98c-2297high2026-08-19
Path traversal in APK: Project export allows arbitrary file write
GHSA-hrpw-vjfw-gq5rmedium2026-08-19
OutOfMemoryError crash when opening a crafted trace database due to unbounded array allocation
GHSA-p4ff-f27r-j8q7medium2026-08-19
Heap-buffer-overflow in TypeFactory::getBase() during jump table recovery
GHSA-v6c3-h9cp-3whfCVE-2026-52759medium2026-06-08
Uncontrolled Resource Consumption in MachoLoader
Sources: GitHub repository advisories · checked 2026-10-20.
UNIX-like reverse engineering framework
Command-line reverse engineering framework with a disassembler, debugger, hex editor and scripting for many architectures and file formats.

Pattern matching for malware research
Tool and rule language from VirusTotal to identify and classify malware samples using textual and binary patterns plus conditions.
Reverse engineering tool for Android APK files
Decodes Android APK resources and code to a near-original form (smali) and rebuilds them after modification, for analysis and testing.

Dynamic instrumentation toolkit
Injects a JavaScript engine into running processes on Windows, macOS, Linux, iOS and Android to trace, hook and modify functions at runtime.

Memory forensics framework
Framework for extracting digital artefacts from memory images (RAM dumps) of Windows, Linux and macOS systems, rewritten in Python 3.